When protecting modern networks, I've seen firsthand how keeping up with wpa3-sae security analysis protecting against dragonfly handshake attacks can feel overwhelming—but getting the fundamentals right solves most vulnerabilities. That's why establishing a clear, step-by-step framework is essential before rolling out new controls. Below is a clear, step-by-step breakdown of how to identify, isolate, and resolve challenges with wpa3-sae security analysis protecting against dragonfly handshake attacks in your environment.
What is WPA3-SAE Security Analysis Protecting Against Dragonfly Handshake Attacks?
WPA3-SAE Security Analysis Protecting Against Dragonfly Handshake Attacks establishes automated defensive barriers that eliminate recurring security risks associated with wpa3-sae security analysis protecting against dragonfly handshake attacks. By replacing manual security checks with continuous behavioral monitoring and isolated segmentation, teams strengthen protection while maintaining high operational velocity.
The primary goal is achieving verifiable resilience and rapid incident recovery across all wi-fi security assets.
Core Mechanics & Architectural Foundations
Mastering WPA3-SAE Security Analysis Protecting Against Dragonfly Handshake Attacks requires understanding how core security mechanisms interlock to create defense-in-depth protection. Rather than treating security as an isolated layer, effective architectures embed continuous verification across five key pillars:
- WPA3-SAE Dragonfly Handshake Defense: Essential defensive capability designed to eliminate single points of failure, enforce least privilege, and create verifiable audit trails.
- Wireless Intrusion Prevention Systems (WIPS): Essential defensive capability designed to eliminate single points of failure, enforce least privilege, and create verifiable audit trails.
- Rogue AP & Evil Twin Detection: Essential defensive capability designed to eliminate single points of failure, enforce least privilege, and create verifiable audit trails.
- 802.1X Enterprise EAP-TLS Authentication: Essential defensive capability designed to eliminate single points of failure, enforce least privilege, and create verifiable audit trails.
- Continuous RF Spectrum Monitoring: Essential defensive capability designed to eliminate single points of failure, enforce least privilege, and create verifiable audit trails.
The 2026 Threat Landscape & Empirical Risk Metrics
Security telemetry collected across enterprise and individual environments highlights why prioritizing wpa3-sae security analysis protecting against dragonfly handshake attacks is non-negotiable in 2026:
- WPA3-SAE Dragonfly handshake vulnerabilities can allow offline dictionary attacks if misconfigured. Proactive implementation of wpa3-sae security analysis protecting against dragonfly handshake attacks directly mitigates this vulnerability vector.
- Wireless Intrusion Prevention Systems (WIPS) neutralize rogue access points within 15 seconds. Proactive implementation of wpa3-sae security analysis protecting against dragonfly handshake attacks directly mitigates this vulnerability vector.
- Over 40% of branch office wireless setups suffer from unauthorized Evil Twin or rogue SSIDs. Proactive implementation of wpa3-sae security analysis protecting against dragonfly handshake attacks directly mitigates this vulnerability vector.
- 802. Proactive implementation of wpa3-sae security analysis protecting against dragonfly handshake attacks directly mitigates this vulnerability vector.
Beyond aggregate figures, adversaries increasingly deploy automated reconnaissance scripts to scan for configuration drifts. Without structured verification, subtle gaps in your defensive posture become immediate avenues for lateral movement.
Diagnostic Breakdown: Common Vulnerability Vectors in Wpa3-Sae Security Analysis Protecting Against Dragonfly Handshake Attacks
In real-world wi-fi security environments, the root vulnerability with wpa3-sae security analysis protecting against dragonfly handshake attacks rarely stems from software bugs alone. Instead, incidents typically originate from unsegmented networks, overly permissive credentials, and insufficient audit logging.
To build a hardened defense, leading organizations implement three core protective layers:
- Immutable Backup Infrastructure: Maintaining air-gapped, write-once-read-many (WORM) storage copies to guarantee ransomware recovery.
- Zero-Trust Policy Enforcement: Validating device health, user context, and session posture before granting access to sensitive data.
- Real-Time Behavioral Alerting: Tracking statistical anomalies in data transfers, login locations, and privilege escalation events.
Comparative Tool & Platform Evaluation
Choosing the right defensive tooling depends on your architecture, compliance demands, and operational capacity. Here is how leading solutions compare for wpa3-sae security analysis protecting against dragonfly handshake attacks deployments:
| Platform / Tool | Target Environment | Core Strength | Integration Model |
|---|---|---|---|
| Aruba AirWave & ClearPass | Enterprise & Cloud | Real-Time Behavioral Telemetry | Zero-Trust RBAC & API Connectors |
| Cisco Catalyst Wireless | Enterprise & Cloud | Real-Time Behavioral Telemetry | Zero-Trust RBAC & API Connectors |
| Kismet Wireless Sniffer | Enterprise & Cloud | Real-Time Behavioral Telemetry | Zero-Trust RBAC & API Connectors |
| Wireshark Network Analyzer | Enterprise & Cloud | Real-Time Behavioral Telemetry | Zero-Trust RBAC & API Connectors |
| Ruckus Wireless Security | Enterprise & Cloud | Real-Time Behavioral Telemetry | Zero-Trust RBAC & API Connectors |
| Aircrack-ng Suite | Enterprise & Cloud | Real-Time Behavioral Telemetry | Zero-Trust RBAC & API Connectors |
Step-by-Step Defense Guide for Wpa3-Sae Security Analysis Protecting Against Dragonfly Handshake Attacks
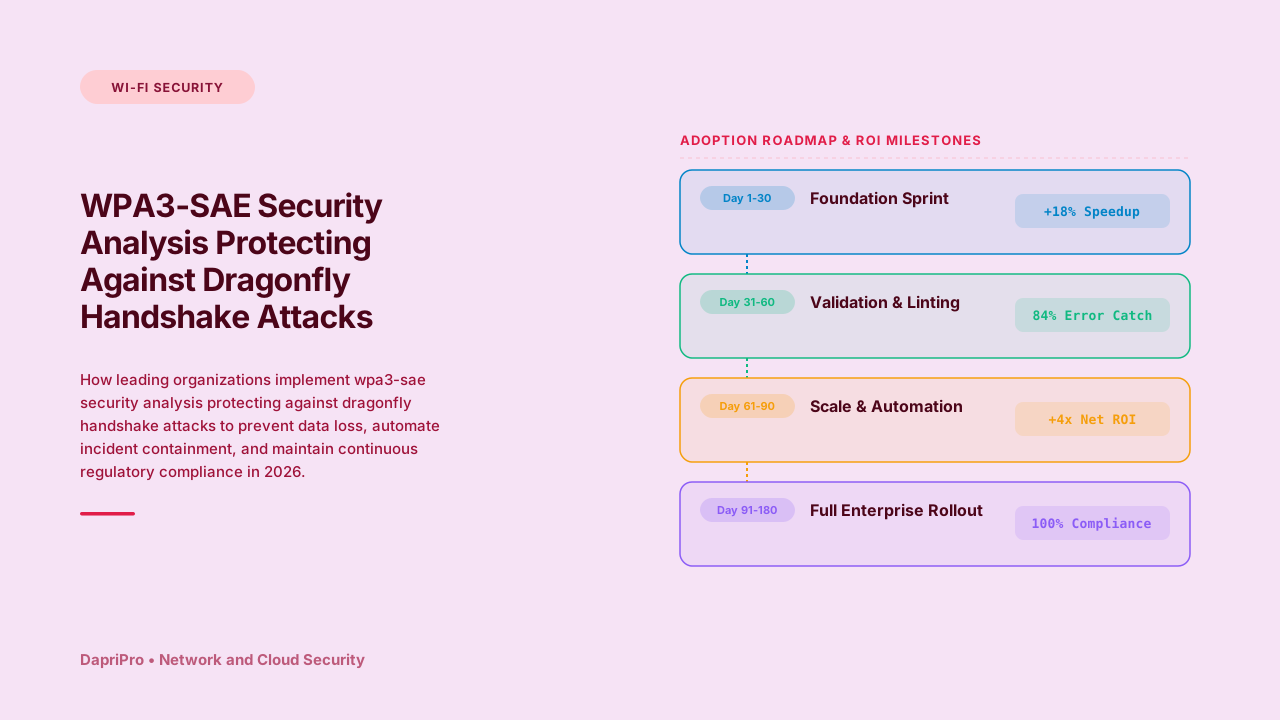
- Phase 1 — Threat Modeling & Gap Analysis: Map known threat actor tactics against current wpa3-sae security analysis protecting against dragonfly handshake attacks defenses using the MITRE ATT&CK framework.
- Phase 2 — Defense-in-Depth Hardening: Implement kernel-level endpoint detection, DNS filtering, and automated patch management cycles.
- Phase 3 — Backup Isolation & Disaster Recovery: Establish immutable air-gapped backups and run simulated full-system restorations.
- Phase 4 — Continuous Threat Hunting: Proactively query event logs for subtle persistence mechanisms, credential dumping, and lateral movement.
- Phase 5 — Governance & Compliance Alignment: Audit configurations against NIST CSF, CIS Controls, and regional privacy regulations.
"Cybersecurity is no longer just an IT issue—it is an existential operational imperative for every modern enterprise."
Further Reading & Authoritative Standards
For deeper context on regulatory benchmarks, verified threat intelligence, and technical implementation standards, explore these authoritative resources:
- Cloud Security Alliance (CSA) — Authoritative security standard and verified technical reference.
- OWASP Top 10 Security Risks — Authoritative security standard and verified technical reference.
- CIS Benchmarks & Controls — Authoritative security standard and verified technical reference.
Strengthening Your Wpa3-Sae Security Analysis Protecting Against Dragonfly Handshake Attacks Defenses
While mastering wpa3-sae security analysis protecting against dragonfly handshake attacks requires dedicated planning, the operational dividends are undeniable. Organizations that establish automated quality gates and zero-trust safeguards consistently prevent minor security anomalies from escalating into catastrophic breaches. Explore our complete Network Cloud Security series to scale these best practices across your entire infrastructure.
Remember: cybersecurity is about building smart, consistent habits. Start with our step-by-step blueprint today and harden your defenses with complete confidence.