What separates a resilient organization from one that suffers catastrophic downtime? In my security assessments, it starts with how effectively you isolate and address bitdefender gravityzone vs sophos intercept x deep architectural comparison. Addressing this early prevents compounding vulnerabilities and gives your team complete peace of mind. Below is a clear, step-by-step breakdown of how to identify, isolate, and resolve challenges with bitdefender gravityzone vs sophos intercept x deep architectural comparison in your environment.
What is Bitdefender Gravityzone Vs Sophos Intercept X Deep Architectural Comparison and How Does It Work?
Bitdefender GravityZone vs Sophos Intercept X Deep Architectural Comparison establishes automated defensive barriers that eliminate recurring security risks associated with bitdefender gravityzone vs sophos intercept x deep architectural comparison. By replacing manual security checks with continuous behavioral monitoring and isolated segmentation, teams strengthen protection while maintaining high operational velocity.
The primary goal is achieving verifiable resilience and rapid incident recovery across all antivirus software assets.
Core Mechanics & Architectural Foundations
Mastering Bitdefender GravityZone vs Sophos Intercept X Deep Architectural Comparison requires understanding how core security mechanisms interlock to create defense-in-depth protection. Rather than treating security as an isolated layer, effective architectures embed continuous verification across five key pillars:
- Instant Cloud Reputation Lookups: Essential defensive capability designed to eliminate single points of failure, enforce least privilege, and create verifiable audit trails.
- Non-Malicious Behavioral Simulation: Essential defensive capability designed to eliminate single points of failure, enforce least privilege, and create verifiable audit trails.
- Server Antivirus Performance Tuning: Essential defensive capability designed to eliminate single points of failure, enforce least privilege, and create verifiable audit trails.
- Signature vs Heuristic Detection: Essential defensive capability designed to eliminate single points of failure, enforce least privilege, and create verifiable audit trails.
- Kernel-Mode File System Interception: Essential defensive capability designed to eliminate single points of failure, enforce least privilege, and create verifiable audit trails.
The 2026 Threat Landscape & Empirical Risk Metrics
Security telemetry collected across enterprise and individual environments highlights why prioritizing bitdefender gravityzone vs sophos intercept x deep architectural comparison is non-negotiable in 2026:
- Cloud-assisted antivirus engines query global reputation databases in under 15 milliseconds. Proactive implementation of bitdefender gravityzone vs sophos intercept x deep architectural comparison directly mitigates this vulnerability vector.
- Behavioral heuristic simulators test antivirus response without executing live malicious binaries. Proactive implementation of bitdefender gravityzone vs sophos intercept x deep architectural comparison directly mitigates this vulnerability vector.
- Server performance tuning and exclusion management prevent I/O bottlenecks across SQL and database hosts. Proactive implementation of bitdefender gravityzone vs sophos intercept x deep architectural comparison directly mitigates this vulnerability vector.
- Modern AV engines achieve 99. Proactive implementation of bitdefender gravityzone vs sophos intercept x deep architectural comparison directly mitigates this vulnerability vector.
Beyond aggregate figures, adversaries increasingly deploy automated reconnaissance scripts to scan for configuration drifts. Without structured verification, subtle gaps in your defensive posture become immediate avenues for lateral movement.
Root Cause Analysis: Why Bitdefender Gravityzone Vs Sophos Intercept X Deep Architectural Comparison Demands Proactive Defense
In real-world antivirus software environments, the root vulnerability with bitdefender gravityzone vs sophos intercept x deep architectural comparison rarely stems from software bugs alone. Instead, incidents typically originate from unsegmented networks, overly permissive credentials, and insufficient audit logging.
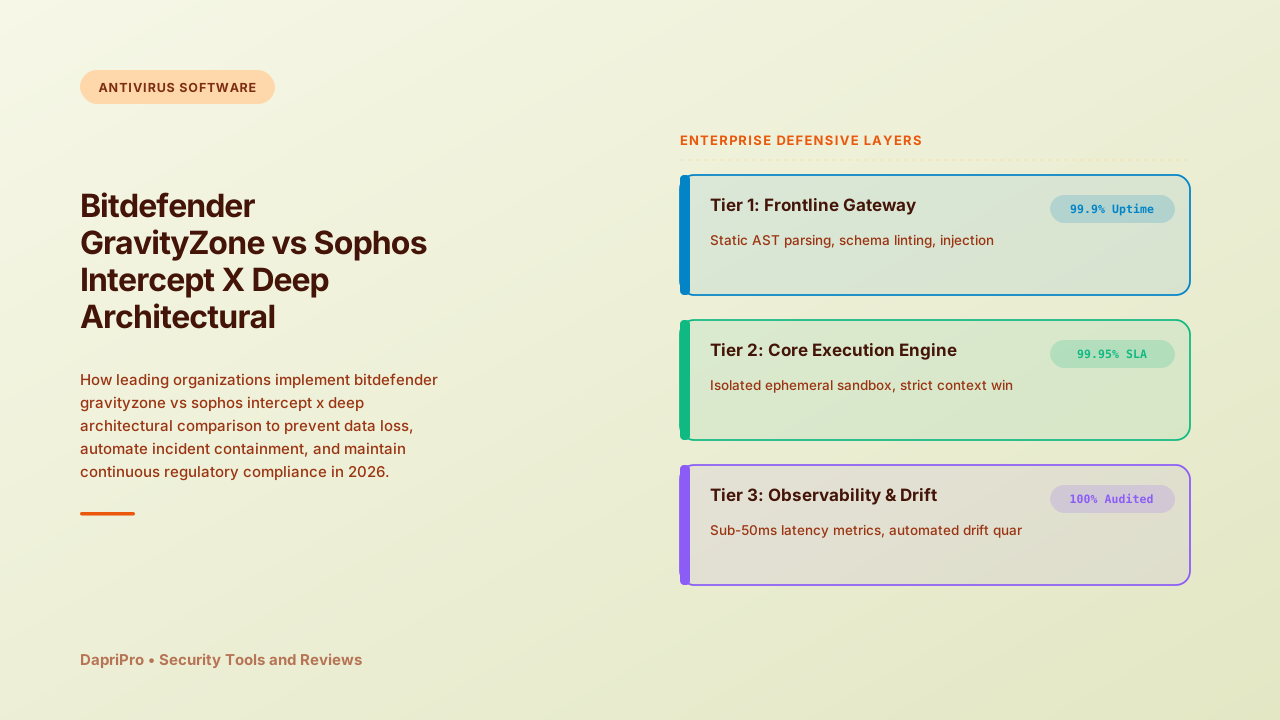
To build a hardened defense, leading organizations implement three core protective layers:
- Identity & Access Hardening: Enforcing phishing-resistant MFA, conditional access policies, and strict role-based access control (RBAC).
- Network Microsegmentation: Isolating critical subnets and workload environments to prevent lateral adversary movement.
- Continuous Telemetry & Auditing: Streaming endpoint and network telemetry to centralized SIEM/SOAR platforms for automated anomaly detection.
Comparative Tool & Platform Evaluation
Choosing the right defensive tooling depends on your architecture, compliance demands, and operational capacity. Here is how leading solutions compare for bitdefender gravityzone vs sophos intercept x deep architectural comparison deployments:
| Platform / Tool | Target Environment | Core Strength | Integration Model |
|---|---|---|---|
| Bitdefender GravityZone | Enterprise & Cloud | Real-Time Behavioral Telemetry | Zero-Trust RBAC & API Connectors |
| Microsoft Defender Antivirus | Enterprise & Cloud | Real-Time Behavioral Telemetry | Zero-Trust RBAC & API Connectors |
| Kaspersky Endpoint Security | Enterprise & Cloud | Real-Time Behavioral Telemetry | Zero-Trust RBAC & API Connectors |
| ESET PROTECT Enterprise | Enterprise & Cloud | Real-Time Behavioral Telemetry | Zero-Trust RBAC & API Connectors |
| Malwarebytes Endpoint Defense | Enterprise & Cloud | Real-Time Behavioral Telemetry | Zero-Trust RBAC & API Connectors |
| Trend Micro Apex One | Enterprise & Cloud | Real-Time Behavioral Telemetry | Zero-Trust RBAC & API Connectors |
Tactical Implementation Blueprint for Bitdefender Gravityzone Vs Sophos Intercept X Deep Architectural Comparison
- Phase 1 — Asset Discovery & Risk Assessment: Conduct a comprehensive inventory of all endpoints, identities, and data flows interacting with bitdefender gravityzone vs sophos intercept x deep architectural comparison.
- Phase 2 — Baseline Architecture & Policy Design: Formulate zero-trust access controls, least-privilege permissions, and automated alerting thresholds.
- Phase 3 — Pilot Rollout & Telemetry Tuning: Deploy controls in high-risk pilot groups to benchmark false-positive rates and train administrative staff.
- Phase 4 — Organization-Wide Production Rollout: Scale policies across all production nodes, integrating event streams with your centralized SIEM/SOAR.
- Phase 5 — Continuous Auditing & Adversarial Simulation: Conduct quarterly tabletop exercises and red-team tests to validate incident containment velocity.
"Passkeys and hardware-backed authentication change the game by making phishing mathematically impossible for traditional credential stealers."
Further Reading & Authoritative Standards
For deeper context on regulatory benchmarks, verified threat intelligence, and technical implementation standards, explore these authoritative resources:
- AV-TEST Security Institute — Authoritative security standard and verified technical reference.
- MITRE Engenuity Evaluations — Authoritative security standard and verified technical reference.
- VirusTotal Public Telemetry — Authoritative security standard and verified technical reference.
Key Takeaways & Next Steps for Bitdefender Gravityzone Vs Sophos Intercept X Deep Architectural Comparison
Sustainable security in 2026 is not about achieving impossible perfection—it is about creating resilient systems that detect, contain, and recover from anomalies before they cause harm. Implementing the tactical steps outlined in this guide ensures your team maintains high velocity while keeping your sensitive assets securely protected. For additional in-depth analyses, visit our dedicated Security Tools Reviews hub.